Cyber Resilience Act guidelines published as reporting obligations come into effect
 Reading time: 3 minutes
The National Cyber Security Centre (NCSC) has published Ireland’s National Cyber Resilience Act (CRA) Guidelines. The guidelines provide practical support for manufacturers as new reporting requirements under the Cyber Resilience Act came into effect across the European Union from Friday.
The publication marks a milestone in the implementation of the Cyber Resilience Act, which introduces mandatory cyber security requirements for products with digital elements placed on the European market.
From 11 September manufacturers are required to report significant vulnerabilities and incidents that impact the security of their products through the EU’s CRA reporting framework.
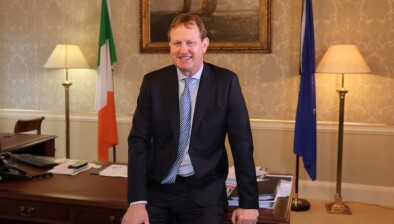
Justice minister Jim O’Callaghan said: “The Cyber Resilience Act represents a major advancement in protecting citizens, businesses and public services from cyber threats. By embedding security requirements into products from the outset and ensuring that significant vulnerabilities and incidents are reported promptly, the Act will help create a safer and more resilient digital ecosystem across Europe.
“The National CRA Guidelines provide practical and welcome support to organisations as these important new obligations take effect.”
The National CRA Guidelines have been developed by the NCSC to support organisations to understand and fulfil their new reporting obligations. They provide practical information on reporting thresholds, timelines, notification procedures and the information required when submitting reports.
Dr Richard Browne, director general of the NCSC, said: “Today marks a significant milestone in European cyber security regulation. The commencement of the Cyber Resilience Act’s reporting obligations will improve visibility of vulnerabilities and incidents affecting connected products and strengthen our collective ability to respond to emerging cyber threats.
“The National CRA Guidelines have been developed to help organisations understand what is expected of them and to support timely and effective compliance. We encourage all manufacturers and relevant economic operators to familiarise themselves with the requirements and ensure that the necessary reporting and vulnerability management processes are in place.”
The CRA establishes a common framework for improving the cyber security of products with digital elements throughout their lifecycle, helping to ensure that cyber security is considered from design and development through to maintenance and support.
Under the Regulation, manufacturers who become aware of an actively exploited vulnerability or a severe incident affecting the security of a product with digital elements must report that information through the CRA Single Reporting Platform. Initial notifications are required within 24 hours of becoming aware of a reportable event, followed by additional reporting in line with the requirements of the Regulation.
The Cyber Resilience Act comes into full effect from 11 December 2027.

Share this article:

Subscribe to our newsletter to not miss articles like this one:
 SUBSCRIBE